During discovery
We ask about your business, your work and your tools. Keep customer records, credentials and sensitive personal information out of the conversation. Redacted samples are enough. See the privacy notice for the website side of this.
During an audit
We work from representative examples, redacted where possible, and read access to the systems in scope. We do not copy your data into our own systems. Working files are deleted at the end of the audit unless you engage us for the build.
During a build
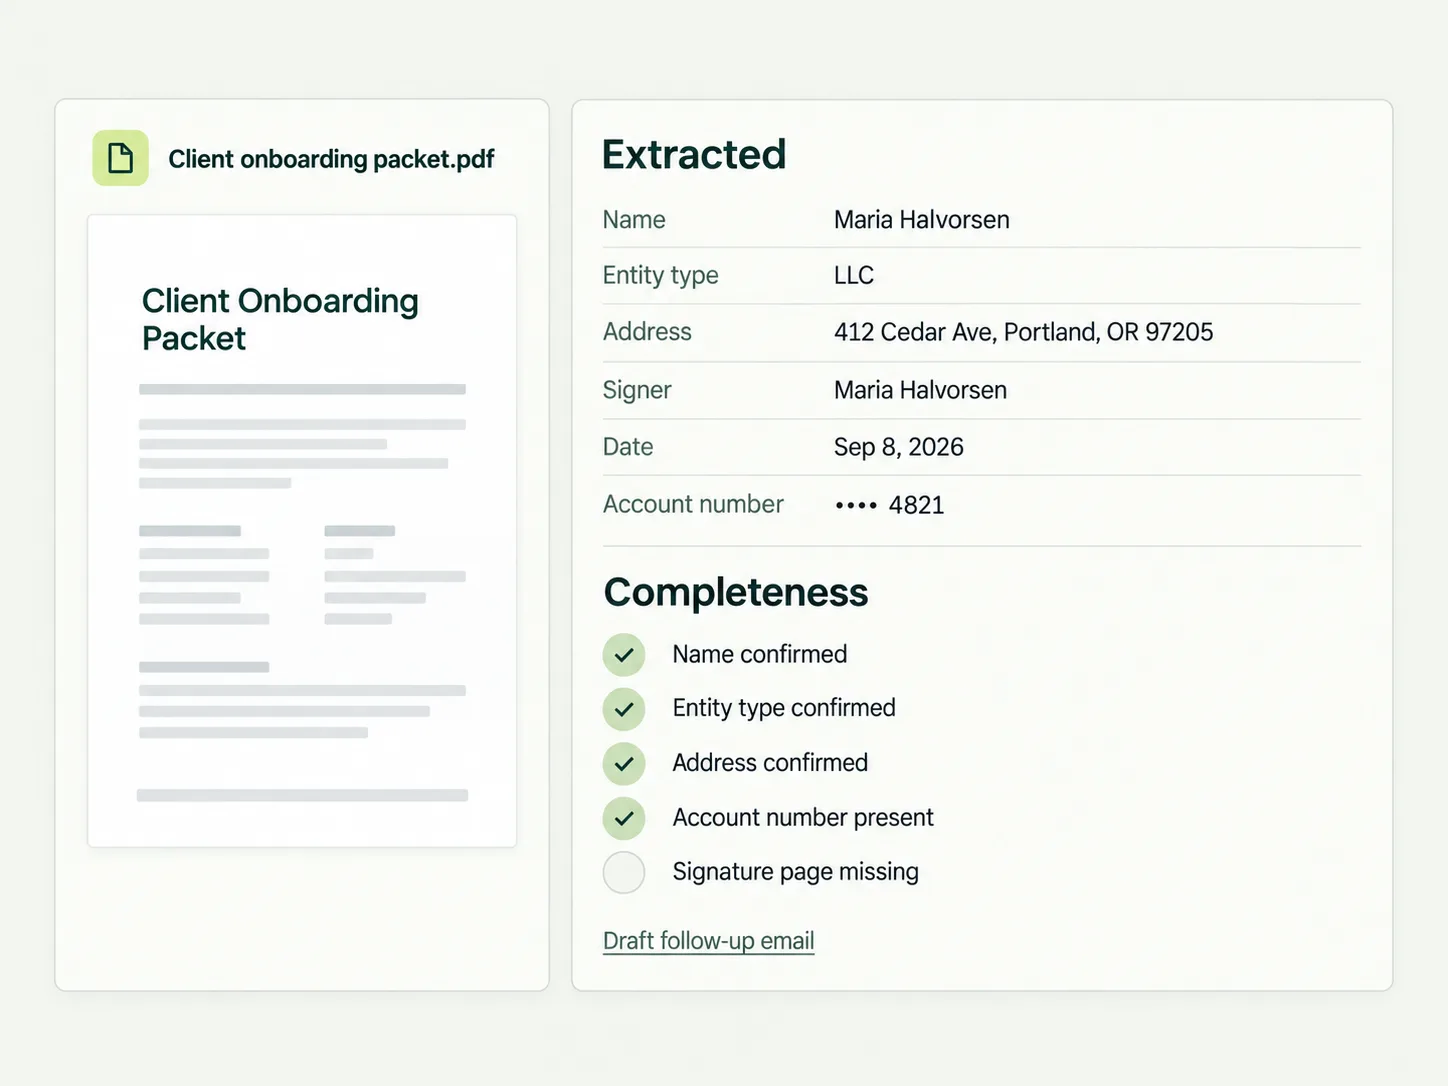
The work runs in your accounts, under permissions you grant, with credentials in your own secret store. Where a cloud AI model is used, we choose the provider with you based on the sensitivity of the work, and we tell you which one. Where the work cannot leave your control, we deploy on-premise private AI instead. We do not use your data to train anything.
After handoff
Your implementation and documentation transfer to you. Our access is revoked and we confirm it in writing. Under a managed AI agents plan, access is limited to what the monitoring requires and is listed in the agreement.
What we do not claim
We do not hold SOC 2, HIPAA, ISO or similar certifications and we will not imply otherwise. If your obligations require an independent security review, it is scoped separately with a specialist.
Questions
Ask before you share anything. Use the contact page.